English-first version 1.3, effective 2 September 2026. It explains how the direct-LAN product, optional account service and hosted payment routes handle data, with no analytics destination enabled.
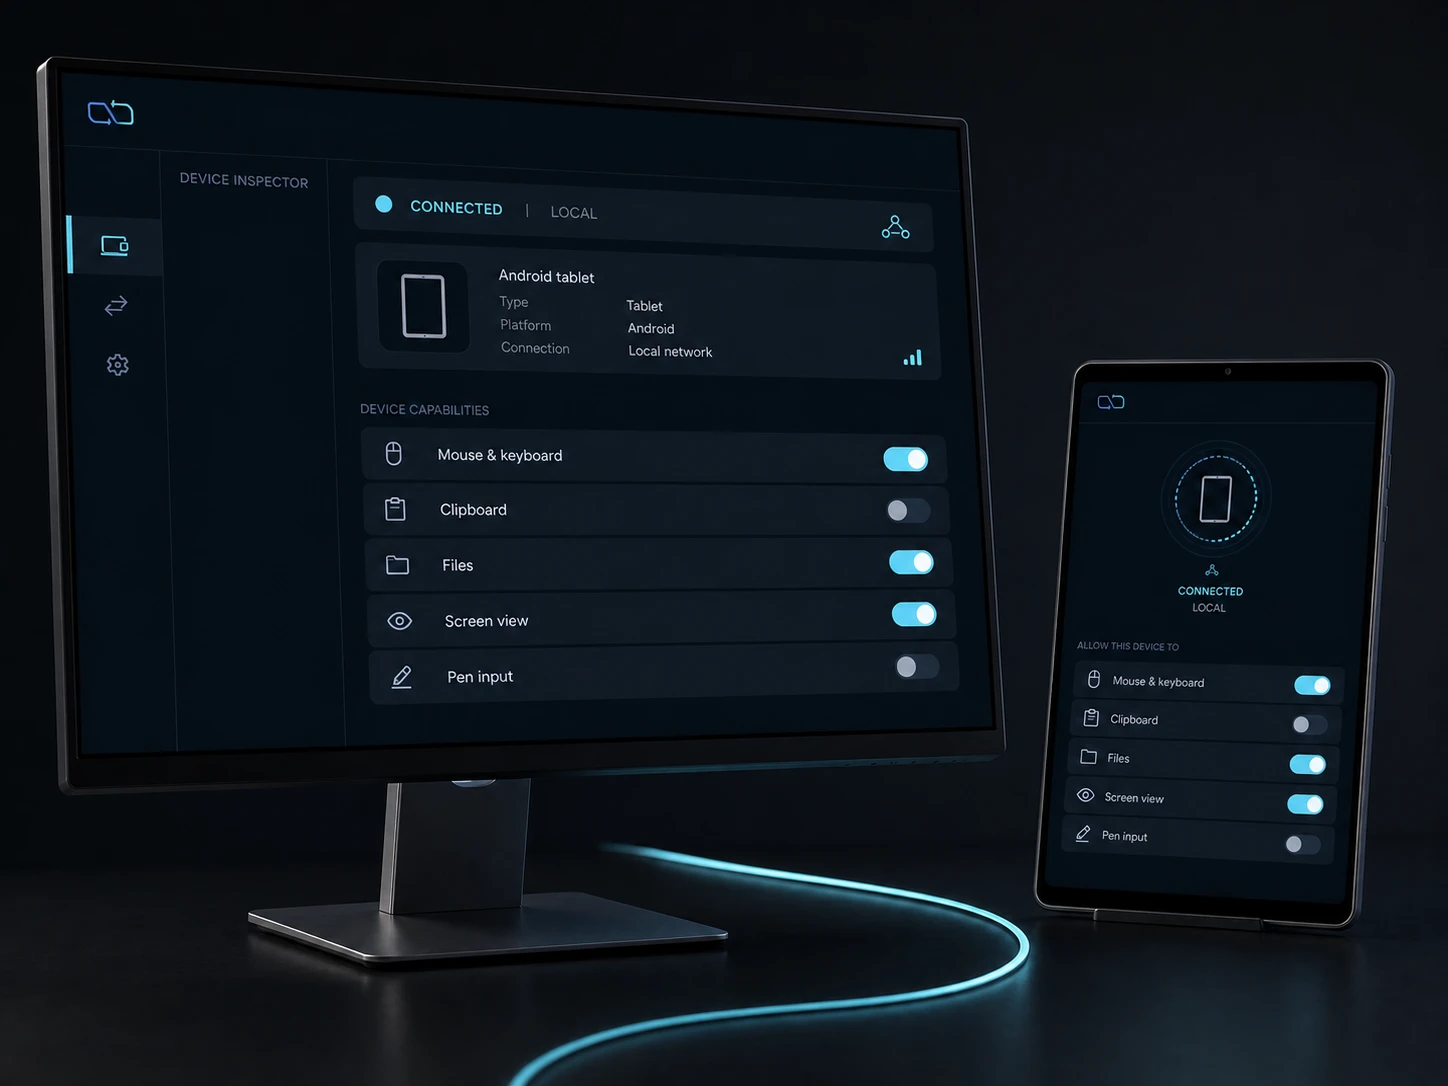
Direct private LAN path. Every capability starts denied.
PLATFORM
Windows 10/11 + Android 10+
NETWORK
Private LAN, no relay
PERMISSIONS
Denied by default
ACCOUNT
Purchases, licenses and recovery
01
01 / CHAPTER
Data controller
The controller for the public DeskChord website and its optional account and hosted payment services is Mateusz Sury, a sole proprietor trading under the business name Mateusz Sury. The business is active in CEIDG and started on 6 August 2026. Registered address: ul. Biedronki 8/2, 05-270 Marki, Poland. NIP: 8961670846. REGON: 545313843. D-U-N-S: 369618965. No analytics service is enabled. Official CEIDG record: https://aplikacja.ceidg.gov.pl/ceidg/ceidg.public.ui/SearchDetails.aspx?Id=0d2d93ac-ff49-43ed-94f0-5aacb001f0de
The installed Windows and Android LAN product remains a separate, local data plane.
Service, complaint, security and privacy requests may be sent to support@deskchord.com. Do not send passwords, recovery codes, full payment-card details or private keys.
Telephone contact: +48 71 707 24 55. Calls may be answered by the DeskChord team or its voicemail service. Do not disclose passwords, recovery codes, full payment-card details or private keys by telephone.
No Data Protection Officer has been appointed. The controller handles privacy requests at support@deskchord.com; the same address accepts complaints and responsible security reports.
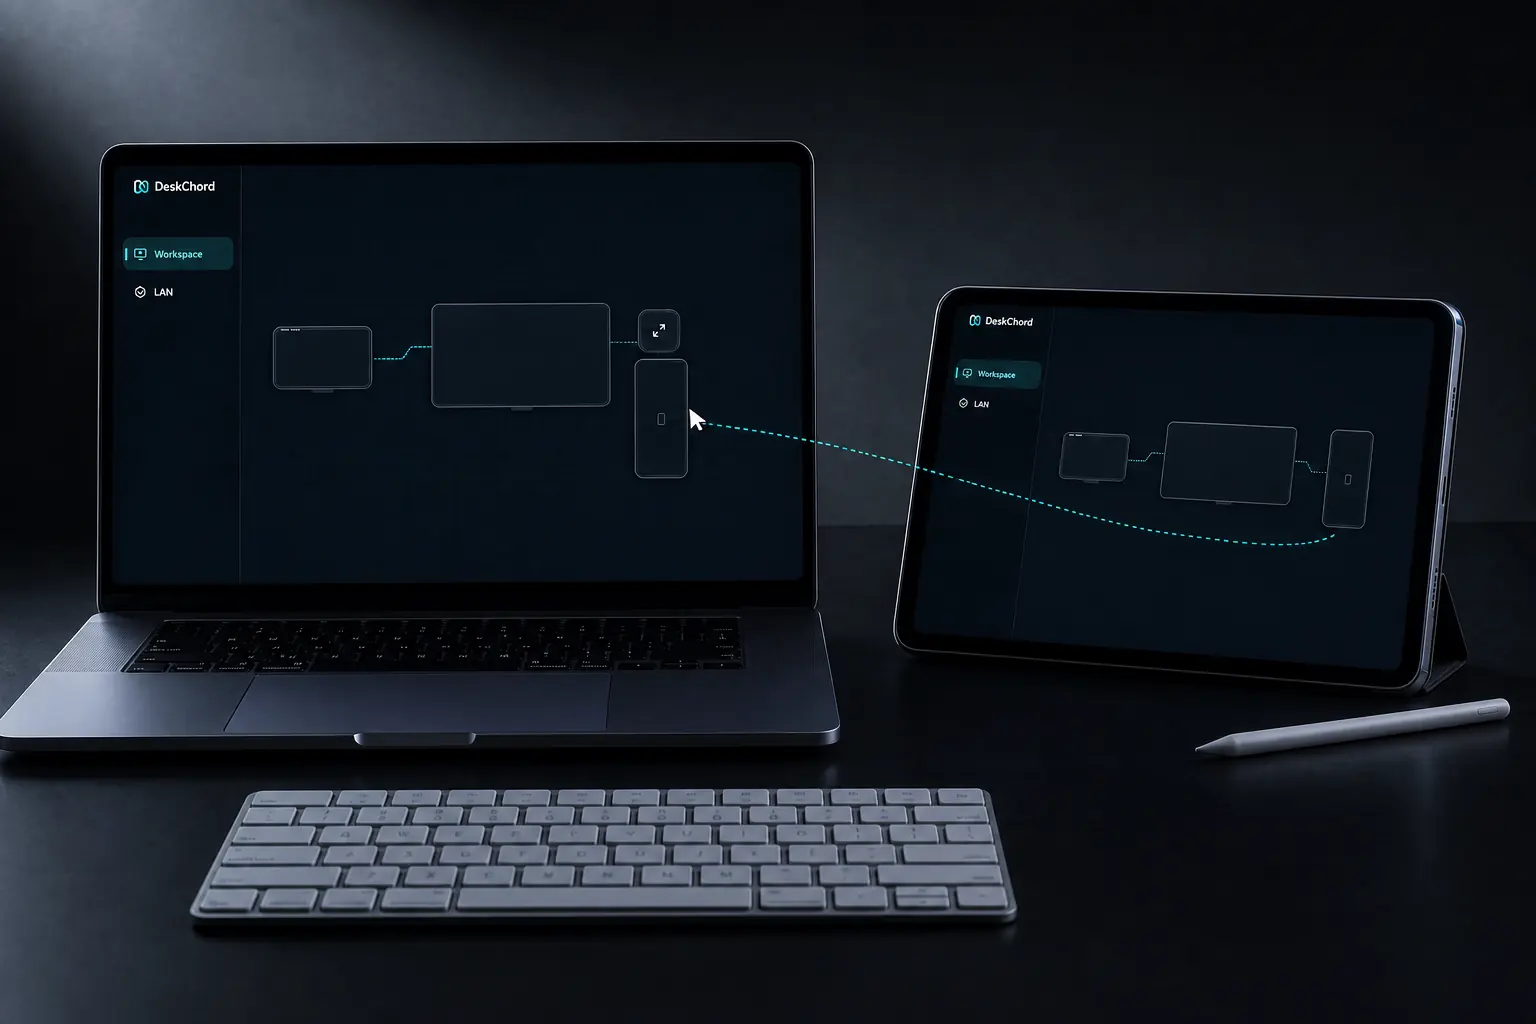
The cursor crosses the shared edge
02
02 / CHAPTER
The installed product keeps its state on each device.
Windows and Android persist protected peer identity, revocable grants and screen topology locally so the LAN product can enforce the choices you made. Windows also keeps a separate, read-only Remote Files export catalog. These stores do not create a cloud copy or grant a capability by themselves.
Platform protection is used for identity and grant records; the LAN data plane remains direct between paired peers.
The export catalog contains selected local roots and bounded metadata, not file contents or raw peer paths.
Received files remain ordinary user files on the destination and are never opened automatically.
One local workspace
03
03 / CHAPTER
The optional web account has a separate purpose.
When the self-hosted account service is enabled, it receives an email address and display name to authenticate a user and manage account, recovery and license actions. Passwords are stored only as scrypt verifiers; recovery codes and session tokens are kept as HMAC digests, with a bounded device label and device-subject hash when device authorization is used.
The account service is not peer authority and does not receive LAN workspace content, clipboard text or file bytes.
Brevo may process transactional account and support email when that channel is enabled; it is not used for LAN content, advertising or analytics. Provider-backed recovery remains disabled unless the account service explicitly advertises it.
Unverified account, recovery and email tokens are retained only for their configured TTL and are rejected after expiry. Account session cookies expire after 7 days, device authorization after 30 days, and recovery codes after 365 days; revocation records may remain without email or display name to reject old offline licenses.
One local workspace
04
04 / CHAPTER
Checkout is hosted and provider-specific.
The paid Pro checkout uses independent hosted payment routes. Stripe provides the card checkout and NOWPayments provides the crypto invoice. Checkout shows only the routes enabled by the current service configuration; the provider selected by the user receives the data necessary for that route and the other provider receives none for that checkout. DeskChord stores only the account and product/plan context, amount and currency, opaque checkout or payment references, status, refund and event digests, and timestamps needed to reconcile an order and issue or revoke a signed license. DeskChord does not receive raw card credentials or wallet private keys.
Stripe receives card details on its hosted page; NOWPayments receives the crypto-invoice data required for its hosted route. DeskChord receives redirects and provider references, then verifies Stripe signed callbacks or performs an authenticated NOWPayments status recheck. The unselected provider receives no data, and no payment provider receives LAN workspace content.
Checkout, account and payment records are excluded from analytics and from the installed LAN runtime. No GA4, PostHog or other analytics destination is enabled.
Retention periods are stated below. The voluntary refund and complaint route is stated in the Terms (sections 5 and 8), while processor safeguards below apply only to the purpose for which each record is kept.
One local workspace
05
05 / CHAPTER
Only functional cookies.
The account service uses one HttpOnly, SameSite=Strict session cookie and one SameSite=Strict CSRF cookie. In local development, the legacy cookies are scoped to /api; production uses host-only __Host-flowmesh_session and __Host-flowmesh_csrf cookies with Secure, Path=/ and no Domain attribute. The session lasts up to 7 days and the CSRF cookie 15 minutes. The public marketing site does not save an analytics choice and has no analytics consent mechanism because analytics is disabled.
No analytics cookie, event, destination or consent record exists; the disabled runtime has no path to enable a provider transfer.
Browser privacy signals cannot enable analytics because no analytics mechanism is present.
Cookies are not used to authorize a LAN peer or capability.
One local workspace
06
06 / CHAPTER
The data plane stays on your LAN.
Windows and Android communicate directly after SAS pairing and pinned mTLS. The local workflow has no relay, cloud drive or remote desktop account in the path.
Peer discovery is limited to the local network.
Bounded terminal sessions and classified Remote Devices serial payloads remain separate-grant, direct-LAN traffic; they are not copied into the public account or any analytics service.
A web account, when self-hosted, does not become peer authority.
Network isolation can block discovery; DeskChord does not bypass it.
One local workspace
07
07 / CHAPTER
Clipboard means bounded text only.
Clipboard participation is an independent grant, active session and exact grant generation. Runtime restart or missing Android IME creates a content-free baseline rather than exporting old text.
Text never enters the WebView.
Revocation, disconnect and replacement drop in-flight values.
Clipboard history, rich formats, files and images are outside the contract.
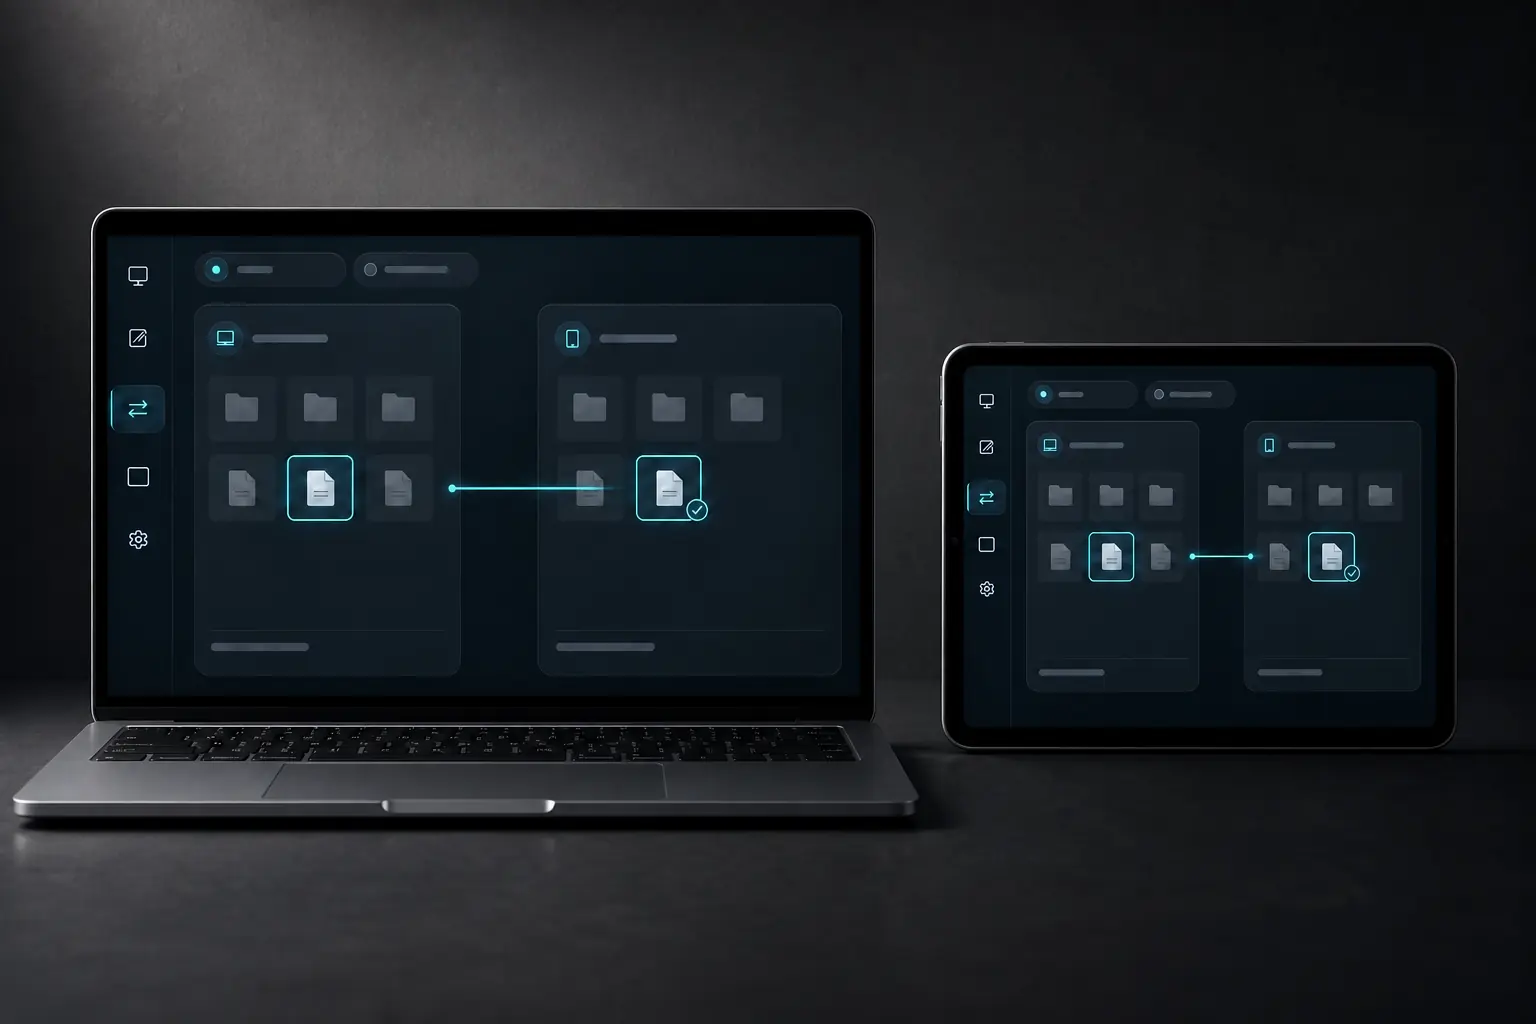
A selected file travels across the local path
08
08 / CHAPTER
Copies leave an auditable boundary.
A file is selected by the user, validated by the receiver and placed as a new copy. Remote Files exposes only a read-only export the user selected through Windows or Android SAF.
No source deletion, move semantics or automatic opening.
Paths are validated and raw peer paths are not advertised.
Provider permission loss closes the export instead of substituting another root.
A selected file travels across the local path
09
09 / CHAPTER
No hidden screen or audio capture.
Interactive View only captures a selected visible source after an explicit Screen View grant. Pen Tablet carries Stylus events without video. Neither lane captures microphone or system audio.
Interactive View touch is an Input-gated per-session opt-in; Pen Tablet remains a separate Stylus route.
Protected content and secure apps can refuse capture.
Virtual display remains unavailable until signed IDD validation.
One local workspace
10
10 / CHAPTER
An optional account stores only what the control plane needs.
Creating an account stores an email address, display name, creation time and a salted scrypt password verifier, never the plaintext password. Recovery codes and session tokens are stored as keyed digests; a device session also keeps its bounded binding hash and user-supplied label.
A browser session is valid for at most 7 days, a named device session for at most 30 days and a recovery code for at most 365 days or until it is used or replaced.
Expired credentials are rejected immediately. Expired sessions and recovery-code digests are pruned during later durable store mutations; an expired digest is never usable.
The self-service export is a convenience copy of the public account record and commercial summaries, never password, recovery, session, audit or issuer secrets; an access request may cover additional personal data subject to lawful security redactions. Deletion removes the personal account, recovery and sessions after revocation; pseudonymous commercial and revocation tombstones remain where needed to reject old offline licences.
One local workspace
11
11 / CHAPTER
Payments use hosted provider pages.
A checkout record links the signed-in account to the provider, product, plan, amount, currency, price reference, status and timestamps. Order, refund, signed-event, license and activation references are retained to fulfil the purchase and prevent a revoked offline entitlement from returning.
Stripe hosts card checkout and NOWPayments hosts the crypto invoice. DeskChord receives redirects, provider references and signed status notifications, not raw card details, wallet credentials or private keys.
A pending checkout expires after 30 minutes. Completed order, refund and revocation records follow the retention schedule in this Privacy Policy.
Contract steps and fulfilment are the basis for requested purchases; fraud prevention, service integrity and legal accounting duties may require limited records. Each payment provider also processes data under its own published privacy terms.
One local workspace
12
12 / CHAPTER
Browser storage is explicit and bounded.
The account service uses a SameSite=Strict session cookie and a 15-minute CSRF cookie. In local development, legacy cookies are scoped to /api; production uses host-only __Host-flowmesh_session and __Host-flowmesh_csrf cookies with Secure, Path=/ and no Domain attribute, with the session cookie HttpOnly. The session lasts up to 7 days.
No analytics cookies, events or choices are added or stored. The public page has no analytics consent mechanism because analytics is disabled.
Browser privacy settings cannot turn on an analytics provider that is not present.
Clearing site data removes browser credentials and functional local state; signing out invalidates the active server session.
One local workspace
13
13 / CHAPTER
No analytics is enabled.
DeskChord currently sends no page or interaction analytics to GA4, PostHog or any other measurement provider. No analytics cookies are set and no analytics event leaves the browser or the LAN product.
GA4, PostHog and other analytics destinations are not processors for the current service and receive no DeskChord data.
No analytics consent mechanism exists and no analytics preference is stored; analytics is disabled at runtime and the public page cannot enable a provider transfer.
Any future measurement would require a separate legal notice, consent flow, processor agreement and retention disclosure before activation.
One local workspace
14
14 / CHAPTER
Purpose, legal basis and source are mapped per service.
Account creation, recovery, licence activation and requested checkout steps use Article 6(1)(b) GDPR to provide the service or take requested steps before a contract. Required accounting records use Article 6(1)(c); narrowly bounded security and abuse records use Article 6(1)(f) to protect users and service integrity.
No public measurement is currently enabled. If a separate measurement service is introduced, it will require prior notice and consent under Article 6(1)(a), with withdrawal stopping future events without affecting earlier lawful processing.
Data comes from the user, the user's browser and signed status messages from the payment provider selected by the user. DeskChord does not enrich it from data brokers.
Providing an email address, display name and password is required only to create an optional account; without them no account can be created. Payment details are required only by the chosen hosted provider to attempt a purchase. No analytics service is enabled, and any future measurement would be optional and would not limit the LAN product, account or purchase.
Account data remains until deletion or the stated credential expiry process. Request addresses are used transiently for bounded in-memory abuse limits and are not written to the account store. The retention schedule below applies to commerce, security, support and legal evidence.
One local workspace
15
15 / CHAPTER
Retention is limited by purpose.
DeskChord keeps each category only for the period needed for its stated purpose and then removes or anonymises it, subject to a documented legal hold.
Unverified account, recovery and email tokens are kept only for their configured time-to-live (TTL), then rejected and removed during bounded store maintenance.
An active account remains until the user requests deletion. On deletion, personal account, recovery and session data are removed or anonymised immediately; encrypted backups expire within 30 days.
Support correspondence is retained for 24 months after the request or case is closed. Security logs are retained for 90 days.
Consent, order, payment, refund and legal evidence is retained for 6 years from the end of the calendar year of the transaction, or longer only while a dispute or mandatory law requires it.
One local workspace
16
16 / CHAPTER
Recipients depend on the feature you choose.
The public service is self-hosted on the operator's HPT infrastructure and placed behind Cloudflare for DNS, TLS and edge delivery. Cloudflare may process request addresses and connection metadata. Stripe and NOWPayments are independent hosted payment processors; Brevo processes account and support email; HaloNet processes support-phone traffic. No analytics provider is enabled.
For each checkout, only a provider shown as enabled and selected by the user receives the information necessary for that route: Stripe hosts card payment, while NOWPayments hosts the crypto invoice and its authenticated status recheck. The other provider receives no data for that checkout; neither receives LAN work content from DeskChord.
Brevo may receive transactional account or support email data when that channel is enabled. HaloNet may process support call metadata or voicemail when the published phone route is used.
Each processor is engaged only under applicable data-protection terms. Where a transfer outside the EEA occurs, Standard Contractual Clauses or another lawful transfer mechanism and supplementary safeguards are documented before activation; only data necessary for the selected purpose is disclosed.
One local workspace
17
17 / CHAPTER
Your rights follow the data, not the interface.
Depending on the processing and applicable law, you may request access, correction, deletion, restriction, portability or objection. No analytics consent is collected or stored because analytics is disabled; there is no analytics consent mechanism to withdraw. We may verify identity before acting on an account request.
Requests, complaints and responsible security reports may be sent to support@deskchord.com. We acknowledge receipt within 2 business days and provide a final response within 14 calendar days. Data-protection rights and statutory deadlines remain controlling where they provide a different or stronger rule.
You may complain to the supervisory authority competent for your habitual residence, place of work or the alleged infringement. In Poland this is the President of the Personal Data Protection Office (UODO), ul. Stanisława Moniuszki 1A, 00-014 Warsaw; current complaint instructions are published at uodo.gov.pl/pl/526/2464.
DeskChord does not use public-site data for advertising profiles or solely automated decisions with legal or similarly significant effects. It is not designed to create child profiles; a purchaser must have legal capacity or valid guardian authority. Responsible security reports may be sent to support@deskchord.com.
One local workspace
FAQ
Clear answers before you install.
Who is the DeskChord data controller?
For the public DeskChord website and its optional account and hosted payment services, it is Mateusz Sury, a sole proprietor trading under the business name Mateusz Sury. The active CEIDG record began on 6 August 2026. Registered address: ul. Biedronki 8/2, 05-270 Marki, Poland. NIP: 8961670846; REGON: 545313843; D-U-N-S: 369618965. No analytics service is enabled. Privacy requests may be sent to support@deskchord.com. Official CEIDG record: https://aplikacja.ceidg.gov.pl/ceidg/ceidg.public.ui/SearchDetails.aspx?Id=0d2d93ac-ff49-43ed-94f0-5aacb001f0de
Is DeskChord analytics enabled?
No. DeskChord currently sends no page or interaction analytics to GA4, PostHog or another measurement provider. No analytics cookies are set and no analytics event leaves the browser or the LAN product.
Does DeskChord upload my files to a cloud service?
No. The data plane is direct-LAN only. Selected files and Remote Files copies stay between paired devices and are verified before local placement.
Does DeskChord keep clipboard history?
No. Clipboard is bounded Unicode text under an independent grant and current session. Rich formats and history are not part of the product contract.
Can a website account see peer addresses?
The optional account service is separate from LAN authority. It does not grant peer access, and the marketing preview never reports a live peer or address.
What does screen view capture?
Only a user-selected visible Windows app or existing display, if the platform permits it. No microphone, system audio or hidden whole-desktop capture is assumed.